

Many companies would benefit from using at least one additional control standard, given their scope and purpose.
The best candidate for most of them is ISO 27017, for cloud services. Almost every organization today is either a cloud customer or a cloud provider. Many are both.
Here’s what these standards add, what that looks like for one real control, and how to start.
Three levels of guidance
Think of the guidance for a control in three levels:
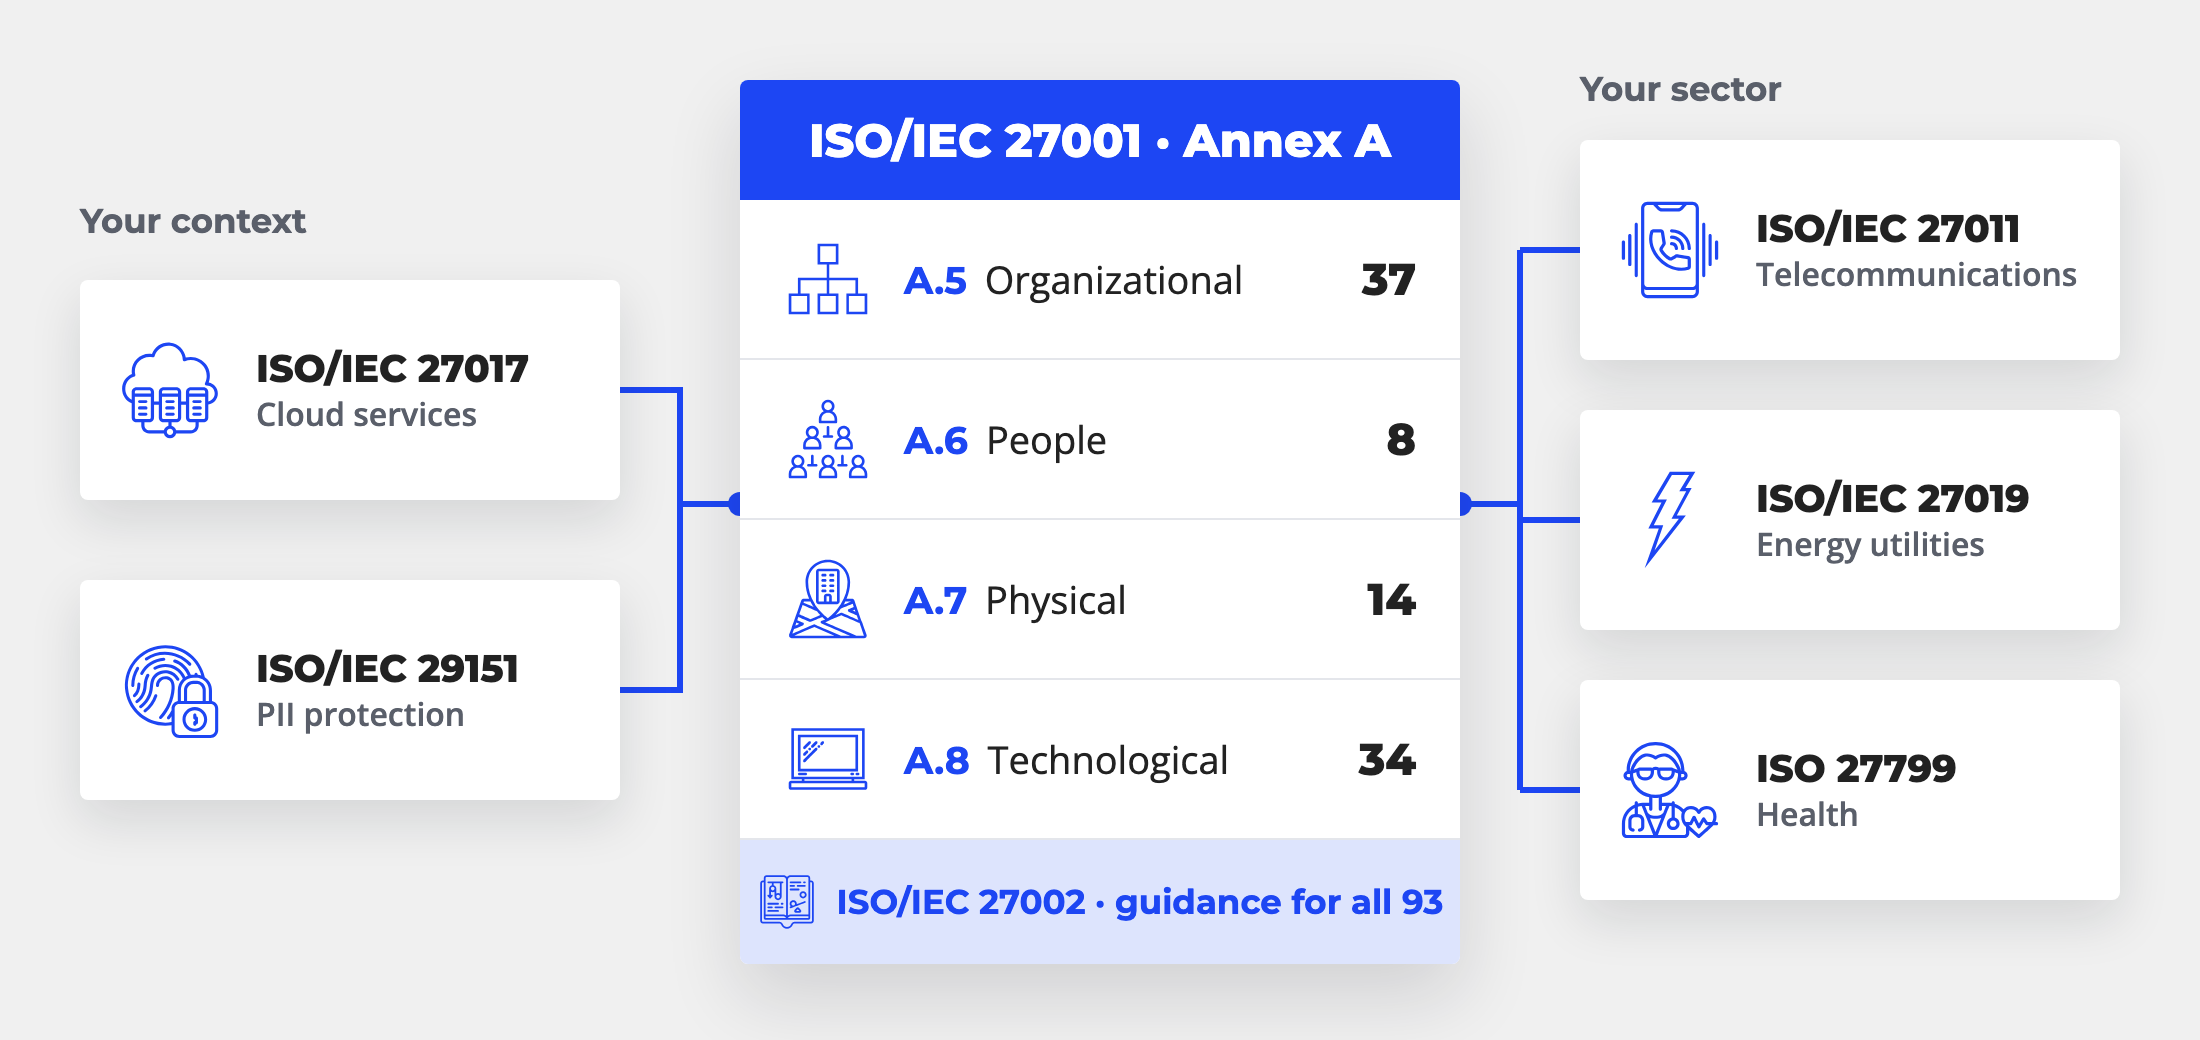
Annex A tells you what. One sentence per control, 93 controls in four chapters: organizational, people, physical, technological.
ISO 27002 tells you how, for everyone. For each control, it gives you a purpose and implementation guidance. It’s written to fit any organization.
The sector and context standards tell you how, for your situation. They take the 27002 guidance, make it more specific for their context, and add controls that 27002 doesn’t have.
ISO/IEC 27000:2026 calls these standards “candidate necessary information security controls” (clause 5.3). Under ISO 27001, clause 6.1.3 b), you can take your controls from any source. Annex A stays the cross-check.