
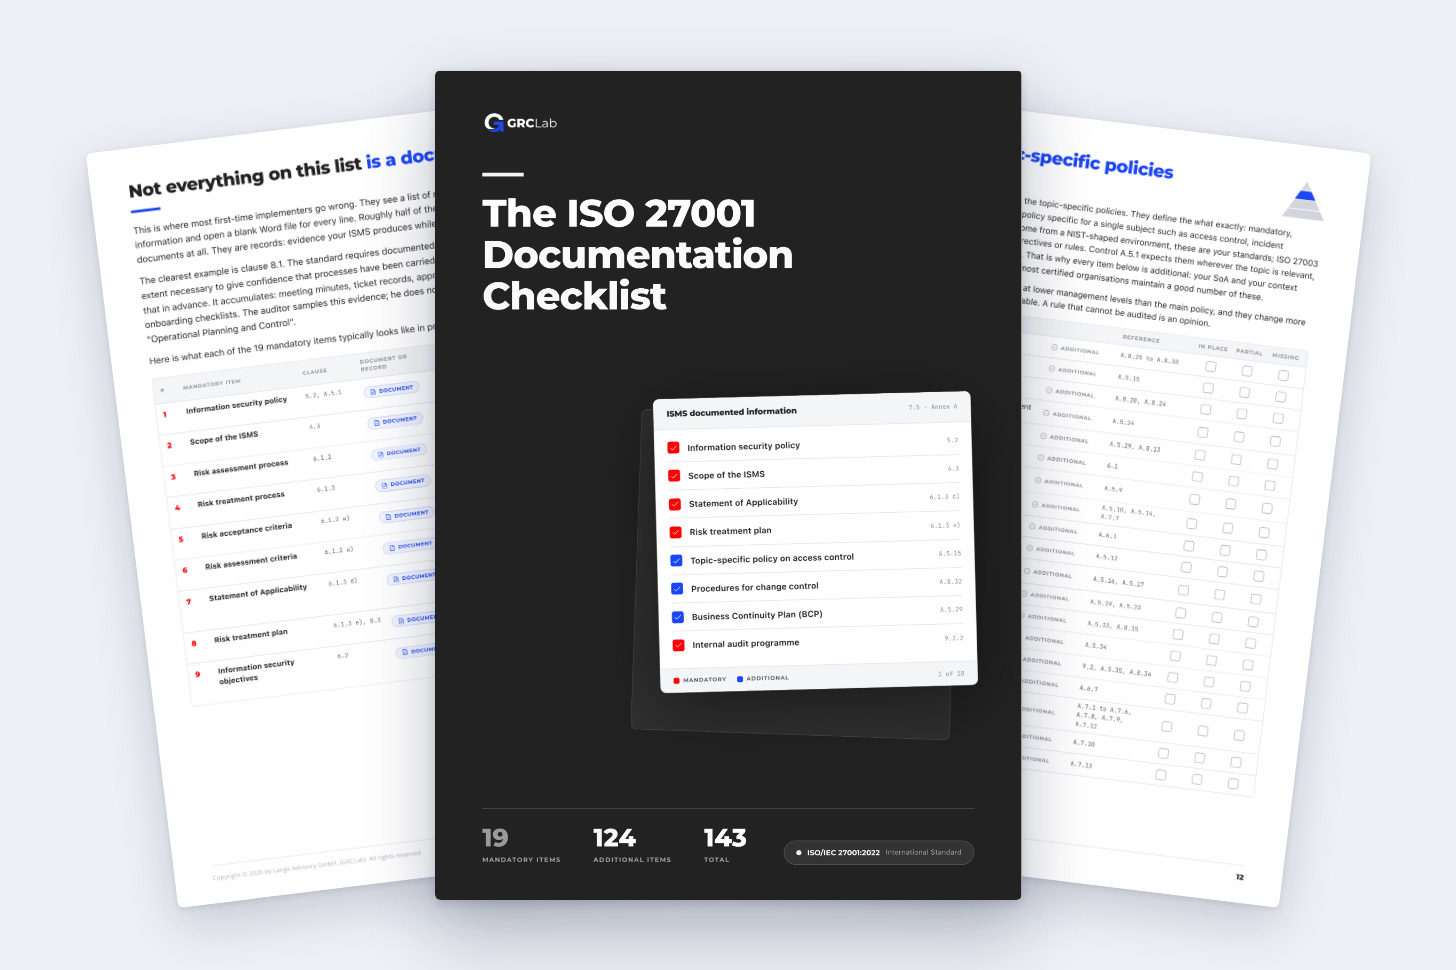
All 143 items an ISMS needs: the 19 the standard demands and the 124 auditors expect, each mapped to its clause or Annex A control.
Most first-time implementers see the list of mandatory documents and open a blank Word file for every line.
That’s the wrong move. Roughly half of the 19 mandatory items aren’t documents at all. They’re records: evidence your ISMS produces while it runs. You write about eight or nine documents. If your documentation project is nineteen Word files, something has gone wrong.
The 19 aren’t where the auditor stops, though. Once you declare an Annex A control applicable in your Statement of Applicability, the auditor expects the policy, procedure or record behind it. That’s where the other 124 come from.
ISO 27001 never collects any of this in one place. The mandatory items are scattered across clauses 4 to 10, named in half sentences. This checklist puts them on one list.
What’s inside the 21-page PDF:
The 19 mandatory items, each with its clause, whether it’s a document or a record, and what it typically looks like in practice
124 additional items in five categories (topic-specific policies, procedures, processes and records), each mapped to its clause or Annex A control
What the auditor actually checks in Stage 1 and Stage 2
A status column for every item (In place, Partial, Missing), so the checklist becomes your gap list
Based on ISO/IEC 27001:2022
One thing it won’t do: the checklist gets you through Stage 1, where the auditor reviews your documented information. Stage 2 is where the auditor stops reading and starts sampling.
I’m Aron Lange, a practising ISO 27001 Lead Auditor. Your auditor already has this checklist. Now you do too.
Subscribe for free below to unlock the download. You’ll also get the GRCLab newsletter, read by 8,000+ GRC professionals: one audit problem every Tuesday and a free live masterclass every Friday at 3 PM Berlin time. You can unsubscribe at any time.